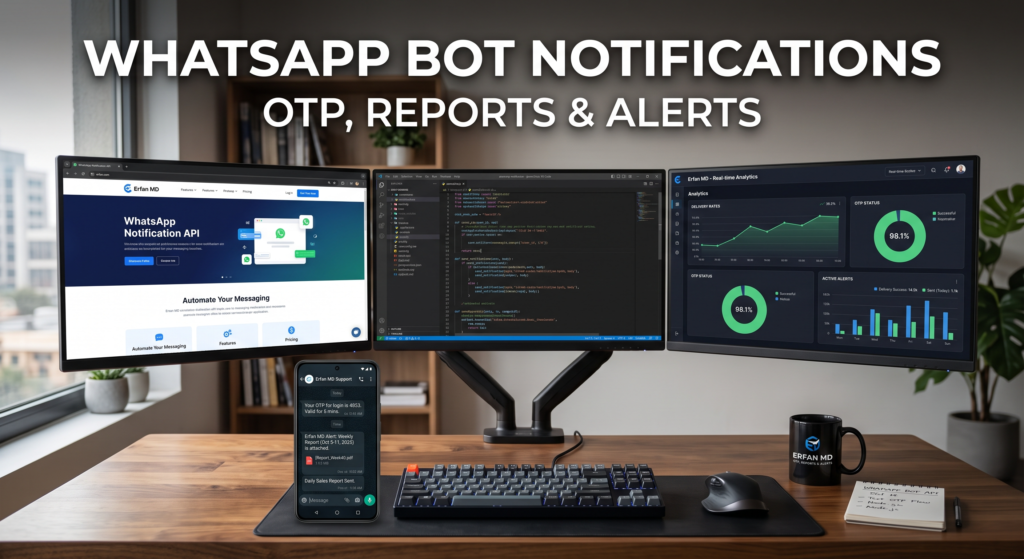
Notifications are useful when they tell a person what happened or what action is needed. They become risky when the data is stale, the recipient is wrong, or a sensitive code is exposed to an untrusted integration.
Separate message types and risk
Order updates should be tied to a verified order event; operational alerts should go to an authorized employee; authentication codes belong in a purpose-built, secure verification flow. Each message type has different data and reliability requirements.
Protect the data path
Check who can trigger a notification, which service receives the data, how logs are retained, and how failed delivery is handled. Keep message content minimal. Do not send passwords or ask customers to share codes with support staff. Use approved providers and authentication products for security-critical messages.
Treat notifications and authentication differently
An ordinary status update and a one-time password have different security requirements. Do not send authentication codes through an unverified third-party automation path; use the official, appropriately secured design for the product and account. For operational alerts, include only necessary details, restrict who can trigger a message, and prevent duplicate or stale events from generating false notifications. Test retries, delivery failures, access logging, and emergency disablement before relying on an automated alert.
Build controls for message accuracy
Require authorization for high-impact alerts, restrict access to the configuration, and test stale, repeated, or out-of-order events. Keep logs useful for diagnosing failures but avoid storing full message contents or secrets unnecessarily. For reports, label the reporting period and data source; for authentication, use an appropriate official secure flow rather than treating a chat message as equivalent. Provide a way to pause notifications immediately if a faulty integration starts sending incorrect messages.
For the next support step, read WhatsApp Customer Support Bot: FAQs and Human Handoffs and compare its handoff and resolution checks with this workflow.
Support workflow checklist
- Map the event that triggers each message.
- Verify recipient identity and source data before sending.
- Keep sensitive data out of message bodies and routine logs.
- Test delivery failure, retry, duplicate-event, and opt-out handling.
A practical scenario
An order alert can say “Order [ID] has shipped” only after the shipping system records the shipment. If the status feed is delayed, hold the message rather than sending a premature notification.
Limits and safeguards
Do not claim that Erfan MD supports OTP delivery, reporting integrations, or transactional notifications unless those functions are implemented and tested. Avoid using unofficial WhatsApp automation for security-critical authentication flows.
Treat each notification type as a separate risk
Use this mini-check on an authorized test setup before relying on this workflow. It is a repeatable test plan, not a claim that Erfan MD has already passed these cases.
- For order alerts, verify the recipient and event against the current order record and send only after the status is confirmed.
- For authentication codes, use an authorized, appropriately protected method, limit exposure, and never route secret codes through an untrusted third-party integration.
- Test expired events, failed delivery, a mismatched recipient, and duplicate triggers so the person receives a clear and safe outcome.
FAQ
Can a WhatsApp bot safely send one-time passwords?
Use an approved authentication design and provider; do not route security codes through an unverified third-party bot.
What should an order alert include?
Only the minimum details needed to identify the event and direct the customer to a secure, appropriate next step.
Primary sources
- WhatsApp Business Messaging Policy
- Meta Terms for WhatsApp Business
- WhatsApp Business Platform pricing documentation
Order updates and authentication messages have different risk profiles. Treat authentication codes as secrets and review the approved, current delivery method before integrating any external service.
Related workflows
- WhatsApp Bot for Ecommerce: Product Questions and Orders — Map an ecommerce WhatsApp workflow for product questions, stock checks, order status, and follow-up without guessing availability or delivery….
- WhatsApp Automation Downtime Plan: Protect the Customer — Use a clear outage checklist to detect failures, switch to manual support, preserve open cases, and resume messaging safely after a bot outage.